Cathay Pacific Says 53,000 Bookings Affected in Amadeus Data Incident
Cathay Pacific says records tied to about 53,000 bookings were accessed through Amadeus. Several other airlines reported affected customer data.
The Amadeus incident has reached multiple major airlines, with Cathay Pacific reporting that travel records linked to around 53,000 bookings were accessed. The exposure varied by customer: booking references, names and flight details were involved in most cases, while a smaller group of records may have included contact details, travel documents or frequent flyer numbers.
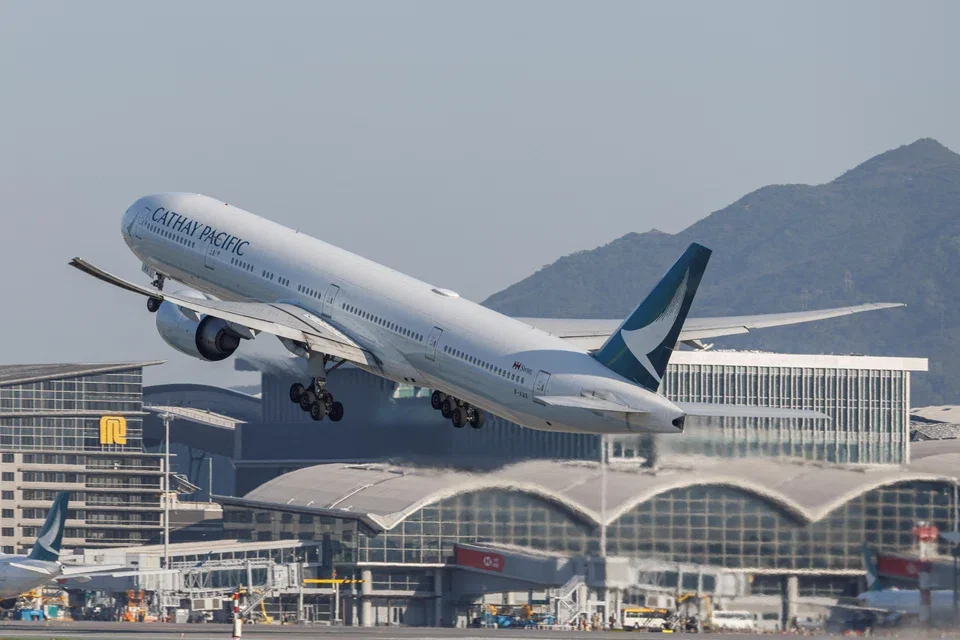
Cathay Pacific said there was no evidence that financial or payment information had been accessed. It also said Amadeus had not identified evidence that the affected data was misused. Those findings describe what the companies had established at the time of their disclosures; Cathay Pacific said its investigation was continuing.
How the exposure occurred
The records were held in a system operated by Amadeus IT Group, which provides technology services to the travel industry. Cathay Pacific said the unauthorised access took place between August 2023 and September 2026, using login credentials assigned to its system account.
The airline said Amadeus notified it on Wednesday, Oct 28, and provided further details the following day. Amadeus said it had contained the incident, reset a password and added monitoring and detection measures to its systems.
The scale reported by Cathay Pacific refers to bookings, not necessarily a count of unique passengers. The airline did not give a breakdown of how many records contained only booking and itinerary information, or how many may have included the additional personal details. That distinction matters to affected customers: an itinerary record can reveal travel plans, while contact or document details may create different kinds of exposure.

Cathay Pacific said the incident had not affected its own systems or operations. It said it would contact affected customers individually once the relevant details were established. The airline also said it had informed the relevant authorities.
Several airlines report exposure
The disclosures extend beyond Cathay Pacific. Korean Air and Asiana Airlines said on Oct 23 that Amadeus had notified them of the incident on Oct 20. Neither airline disclosed how many customers were affected, and both said no secondary damage had been reported at that point.
JAL Group said on Wednesday that about 92,000 customers of Japan Airlines and Japan Transocean Air were affected. ANA Holdings disclosed on Thursday that information belonging to around 37,800 passengers was involved. Jin Air said on Thursday that 1,454 passengers’ personal information was compromised. Its listed data included names, birth dates, mobile phone numbers and nationalities.
Bloomberg reported on Friday that German carrier Condor was also affected. The available disclosures do not provide a complete count across all the airlines, and the reported figures cover different customer groups and data types. They therefore show the breadth of the incident, but do not establish a single total for all affected passengers.
What remains unclear
For customers, the immediate questions are which specific records were accessed, what information each record contained and whether any misuse emerges. Cathay Pacific’s account distinguishes the bulk of affected cases from a smaller subset that may have involved extra personal details. It has not published a count for that subset.
For airlines, the incident highlights a practical exposure created by shared reservation technology: customer records are handled through systems operated by service providers as part of booking and travel processes. When access credentials are used without authorisation, the information at risk can span several carriers, even as each airline separately assesses the records tied to its customers.
Amadeus’s password reset and expanded system monitoring are among the containment steps described by Cathay Pacific. The disclosures do not specify how the credentials were obtained or whether further records could be identified as the review continues. The next useful update will be a clearer account of which customers were affected and what data their individual records contained.
For now, Cathay Pacific’s reported figure is about 53,000 bookings, with no evidence reported of financial or payment information access or data misuse. Other airlines have confirmed exposure, but several have not published customer counts. Those unresolved details will determine how fully passengers and businesses can assess the incident’s reach.


